Three problems consultants do not solve.
Built for the 200-system estate, not the 2-system pilot.
Three estates, three governance models.
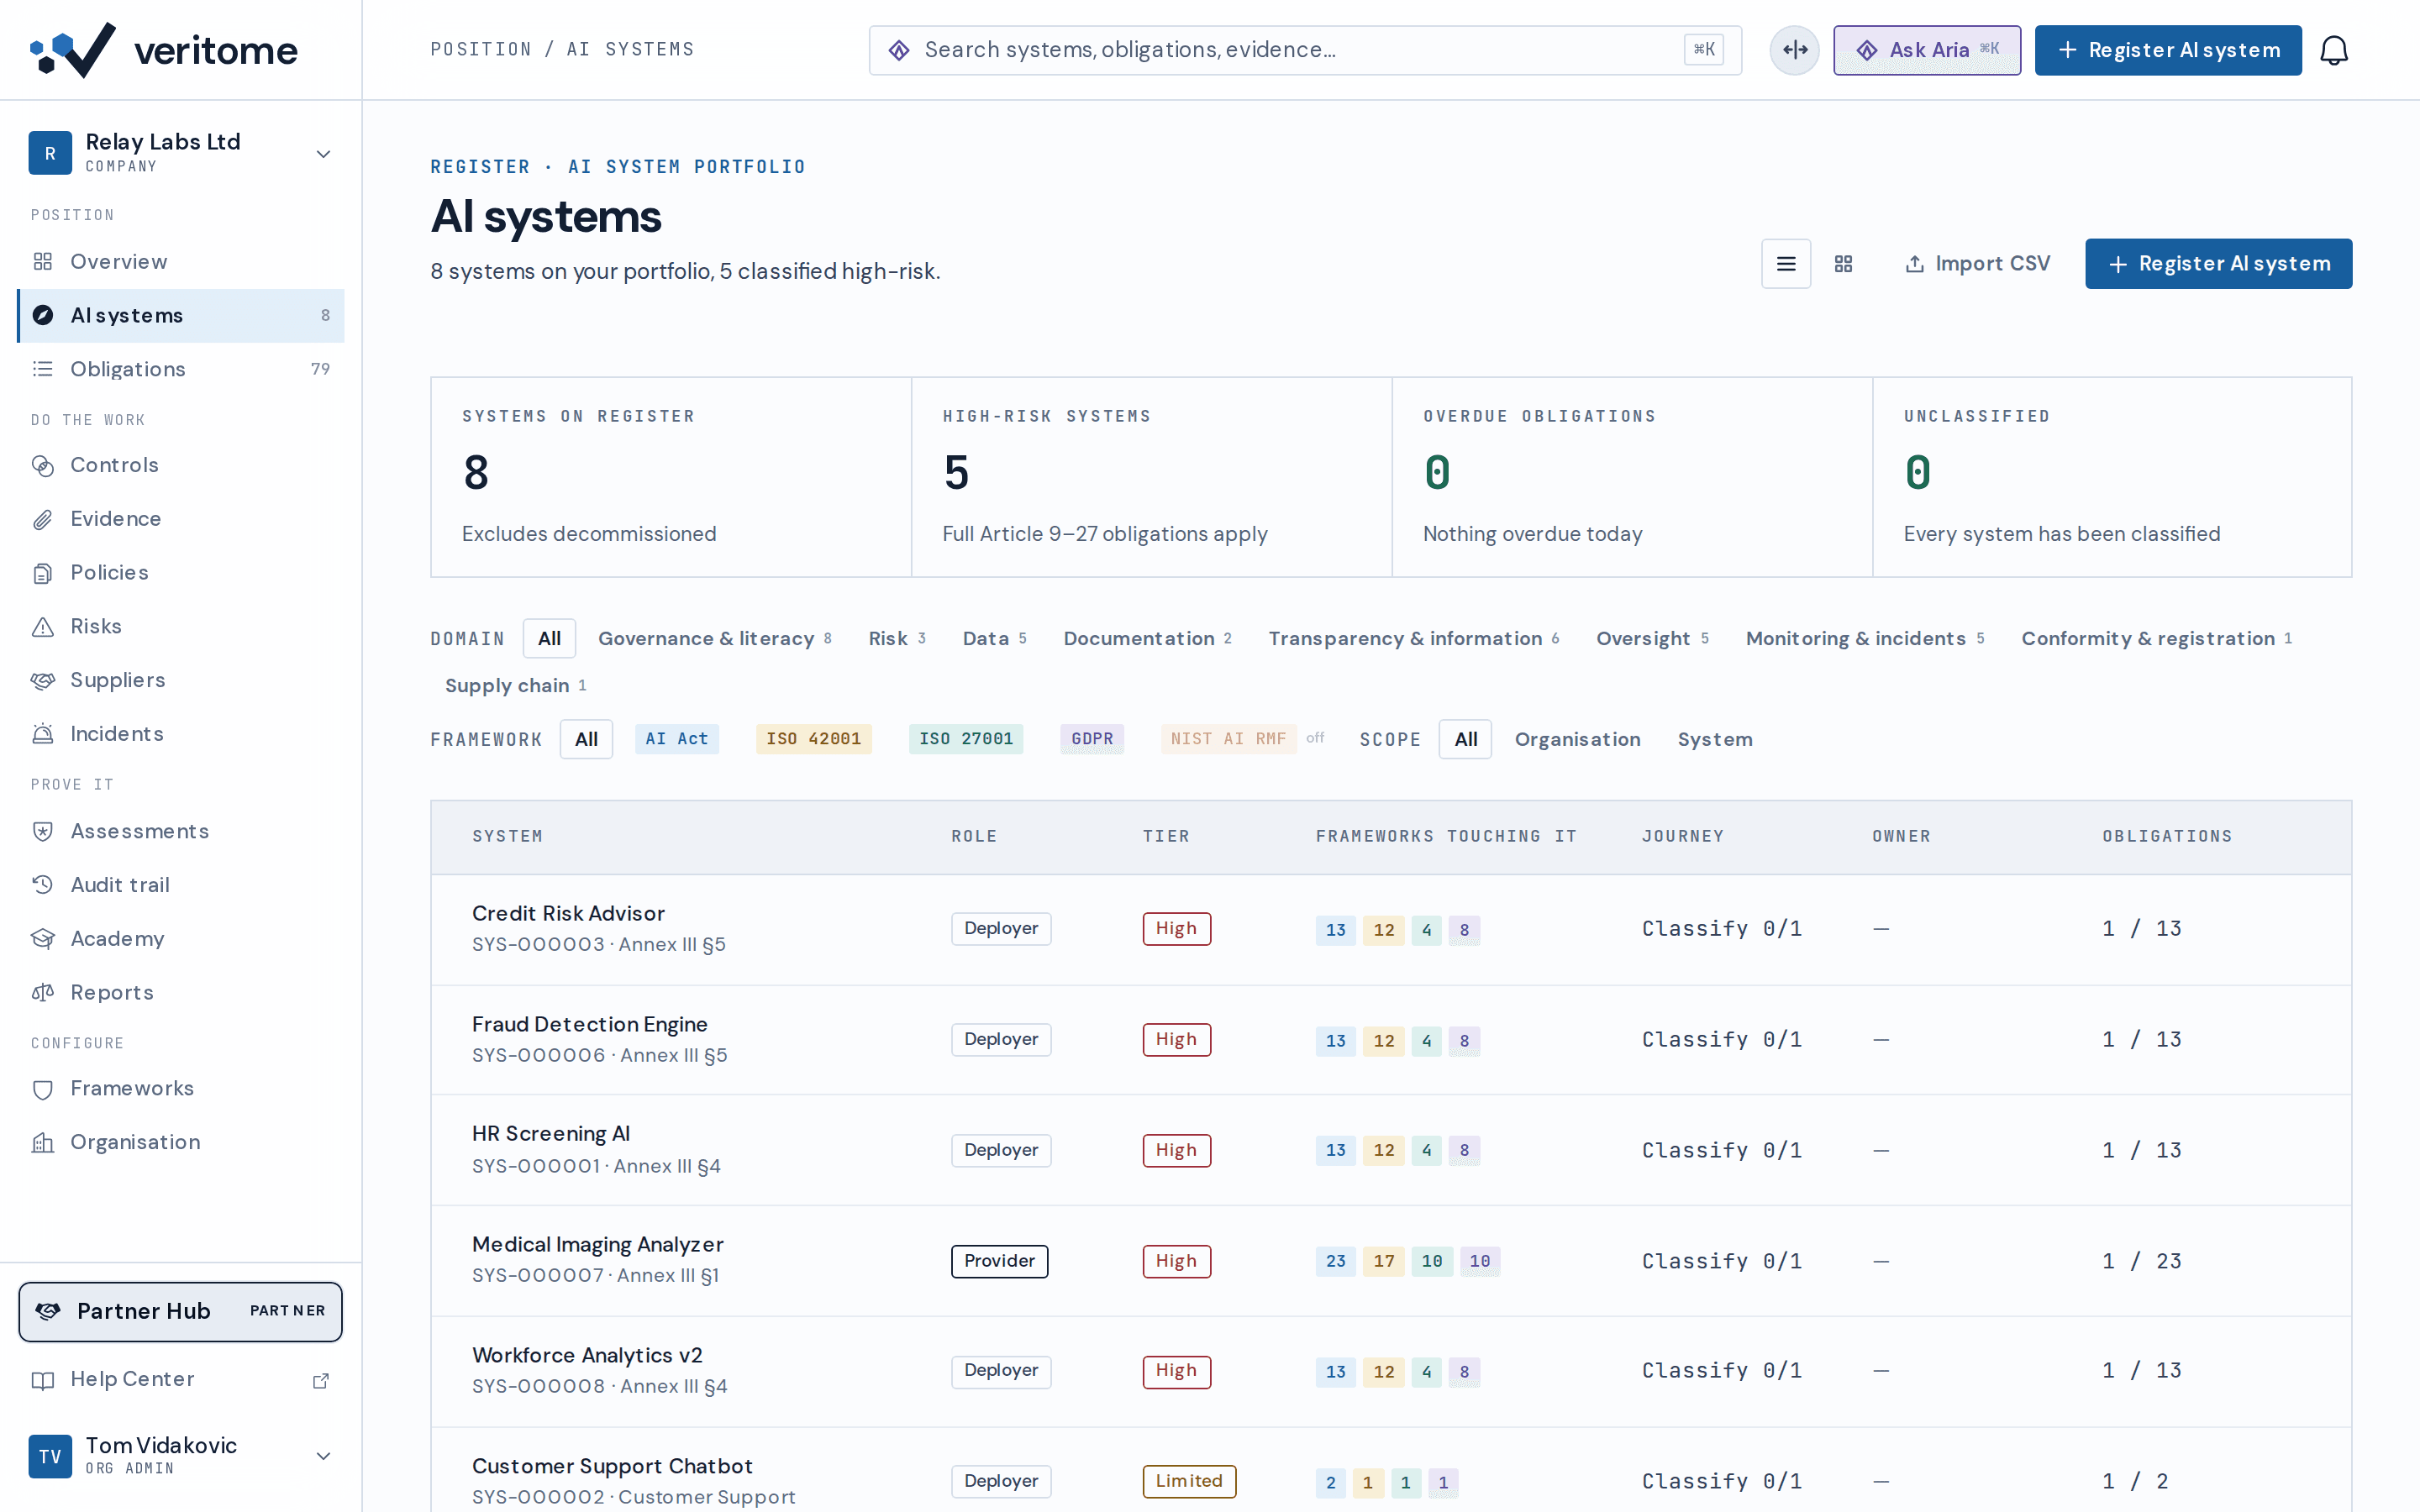
A retail bank with 80 in-house models — provider for proprietary risk models, deployer for vendor systems.
- Separate organisations keep the in-house provider obligations apart from the vendor-deployer obligations.
- The phase-gate view surfaces the systems blocked at Assess — exactly where conformity assessments are pending.
- Each model's Annex IV assembles from the model card, the risk plan and the governance plan.
- The quarterly board pack is the portfolio view, generated as a sealed PDF.
A multinational pharma group with 30 AI systems across R&D, clinical and commercial.
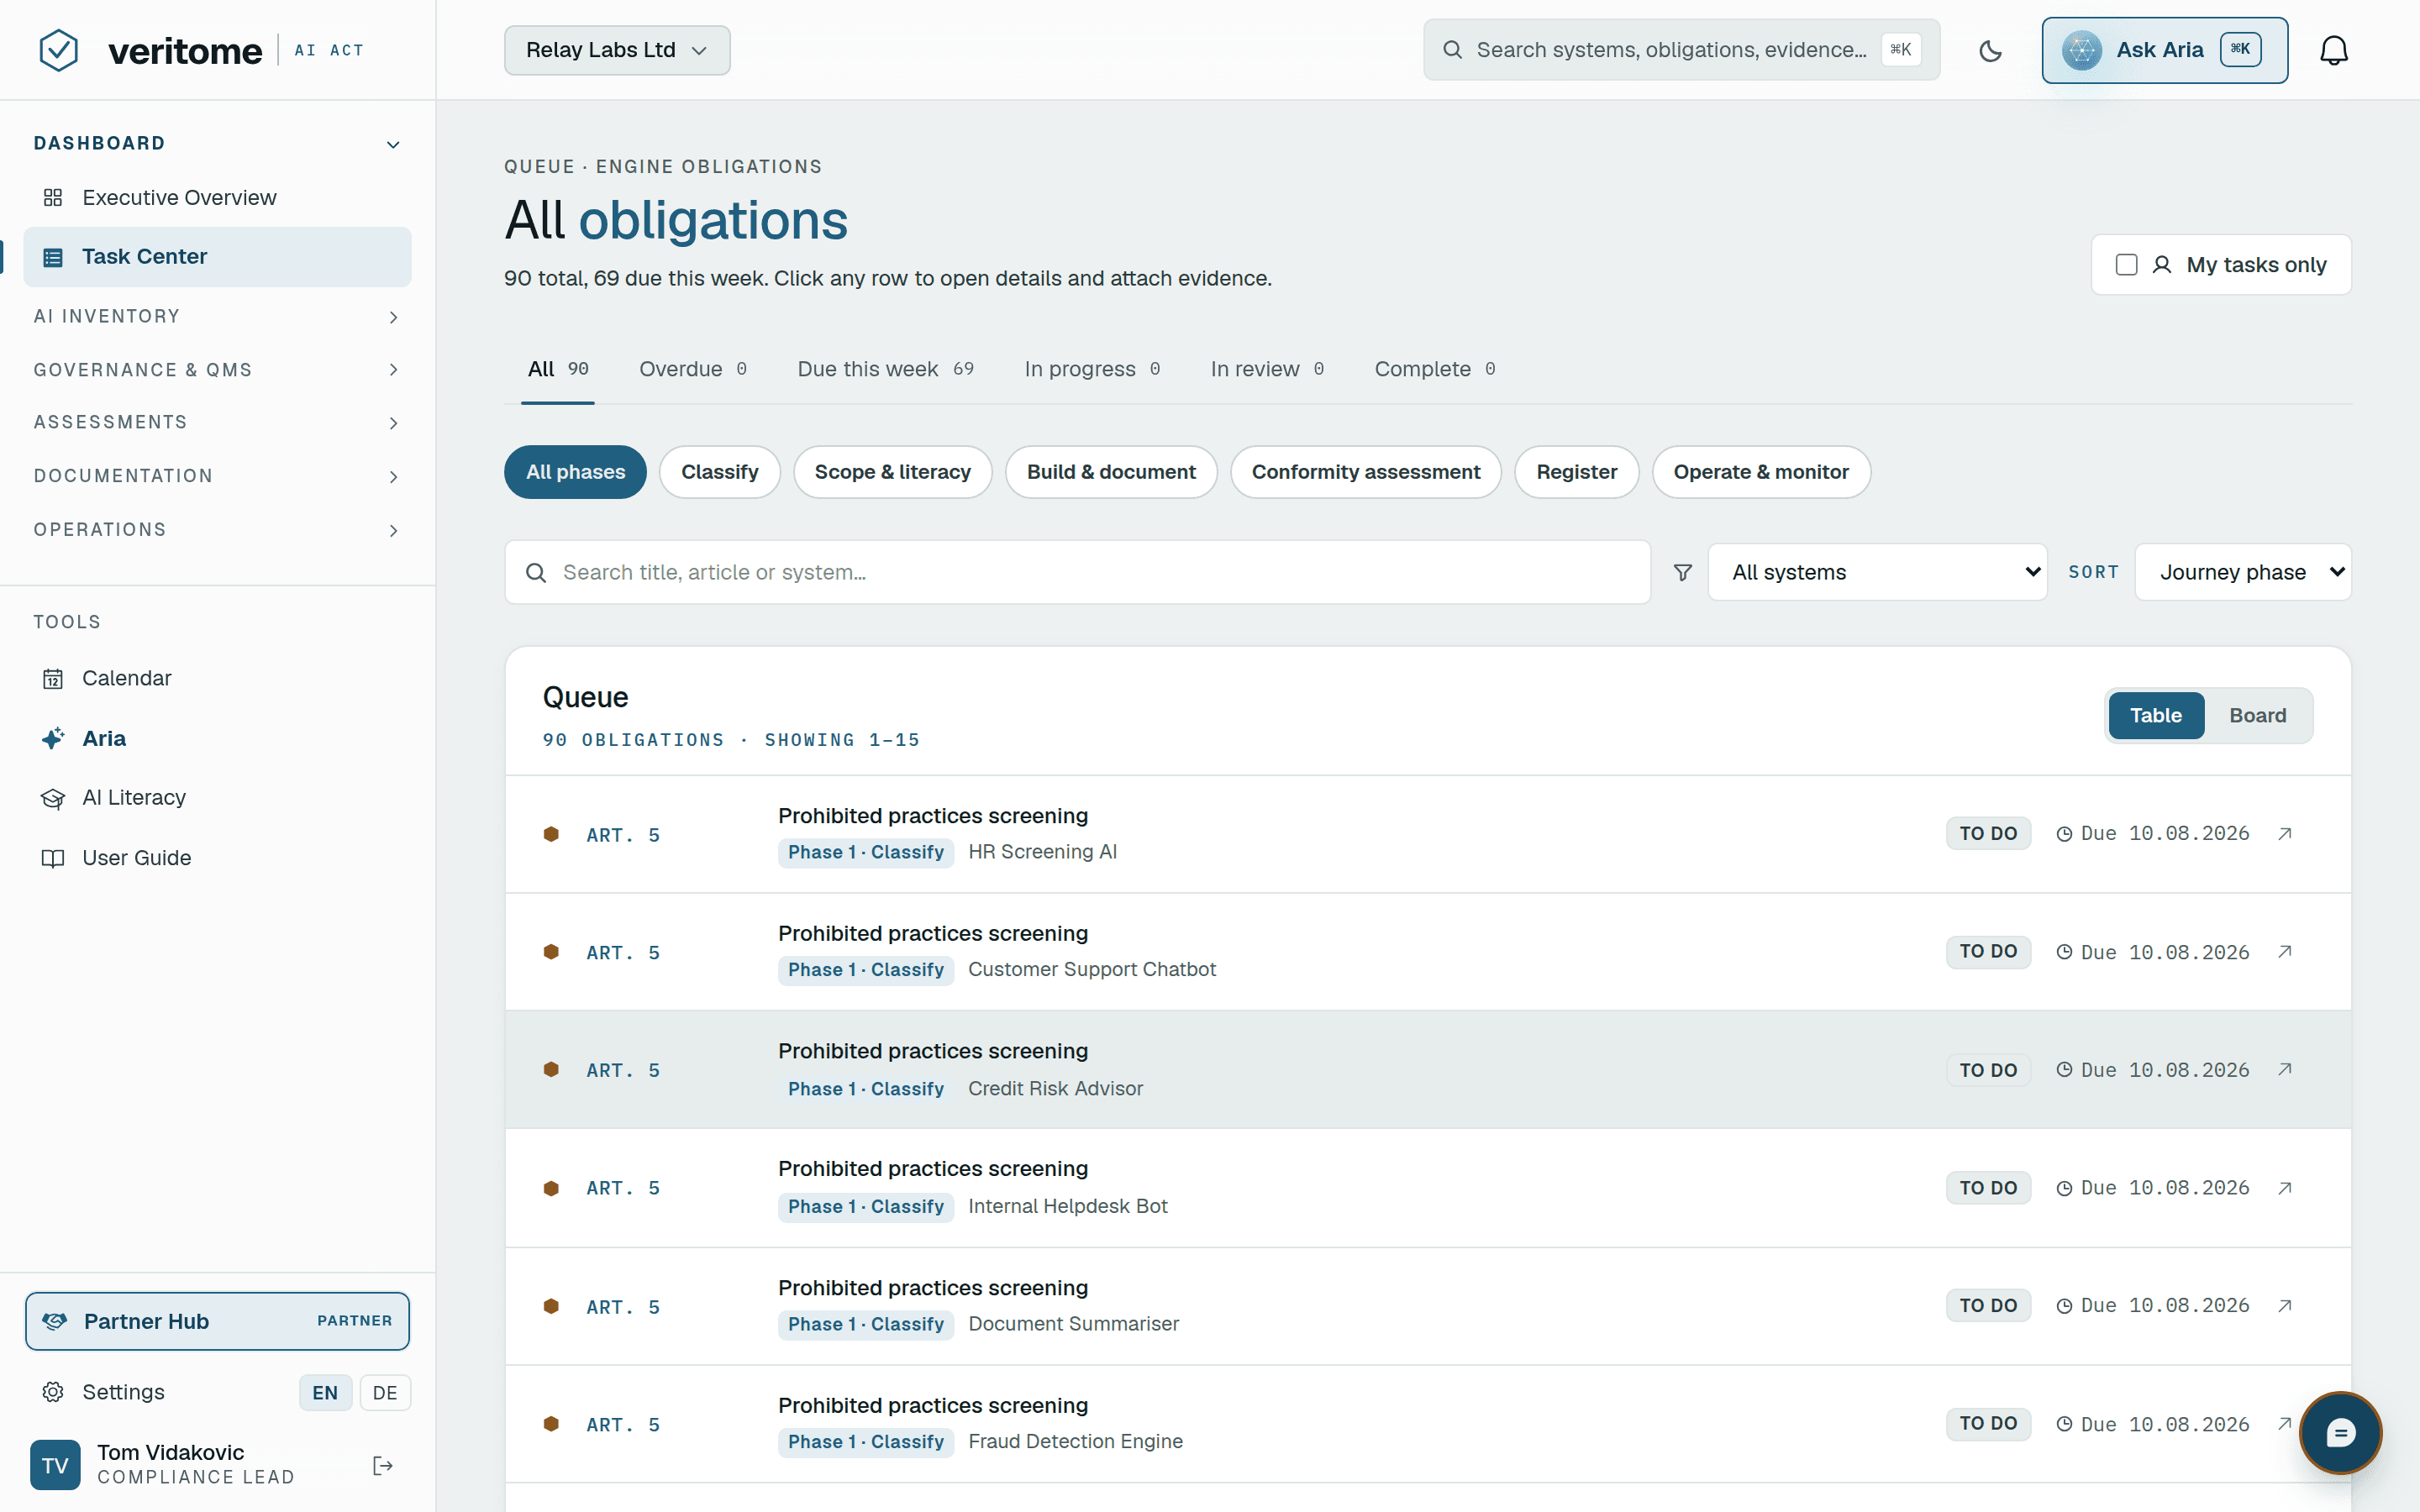
- Annex III §5 (essential services) and §3 (education) systems trigger different obligation sets.
- The FRIA runs for the public-impact systems and is passed on the others.
- The regulator-view dossier is the artefact the authority asks for; the verify URL spares the audit team a dozen email threads.
- The AI-literacy programme is tracked group-wide for the Art. 4 sign-off.
An insurance group consolidating risk management, GDPR and EU AI Act work into one instrument.
- The Art. 9 risk plan integrates with the enterprise risk register via the API.
- Residual sign-off feeds the Solvency II ORSA narrative — same evidence, two regimes.
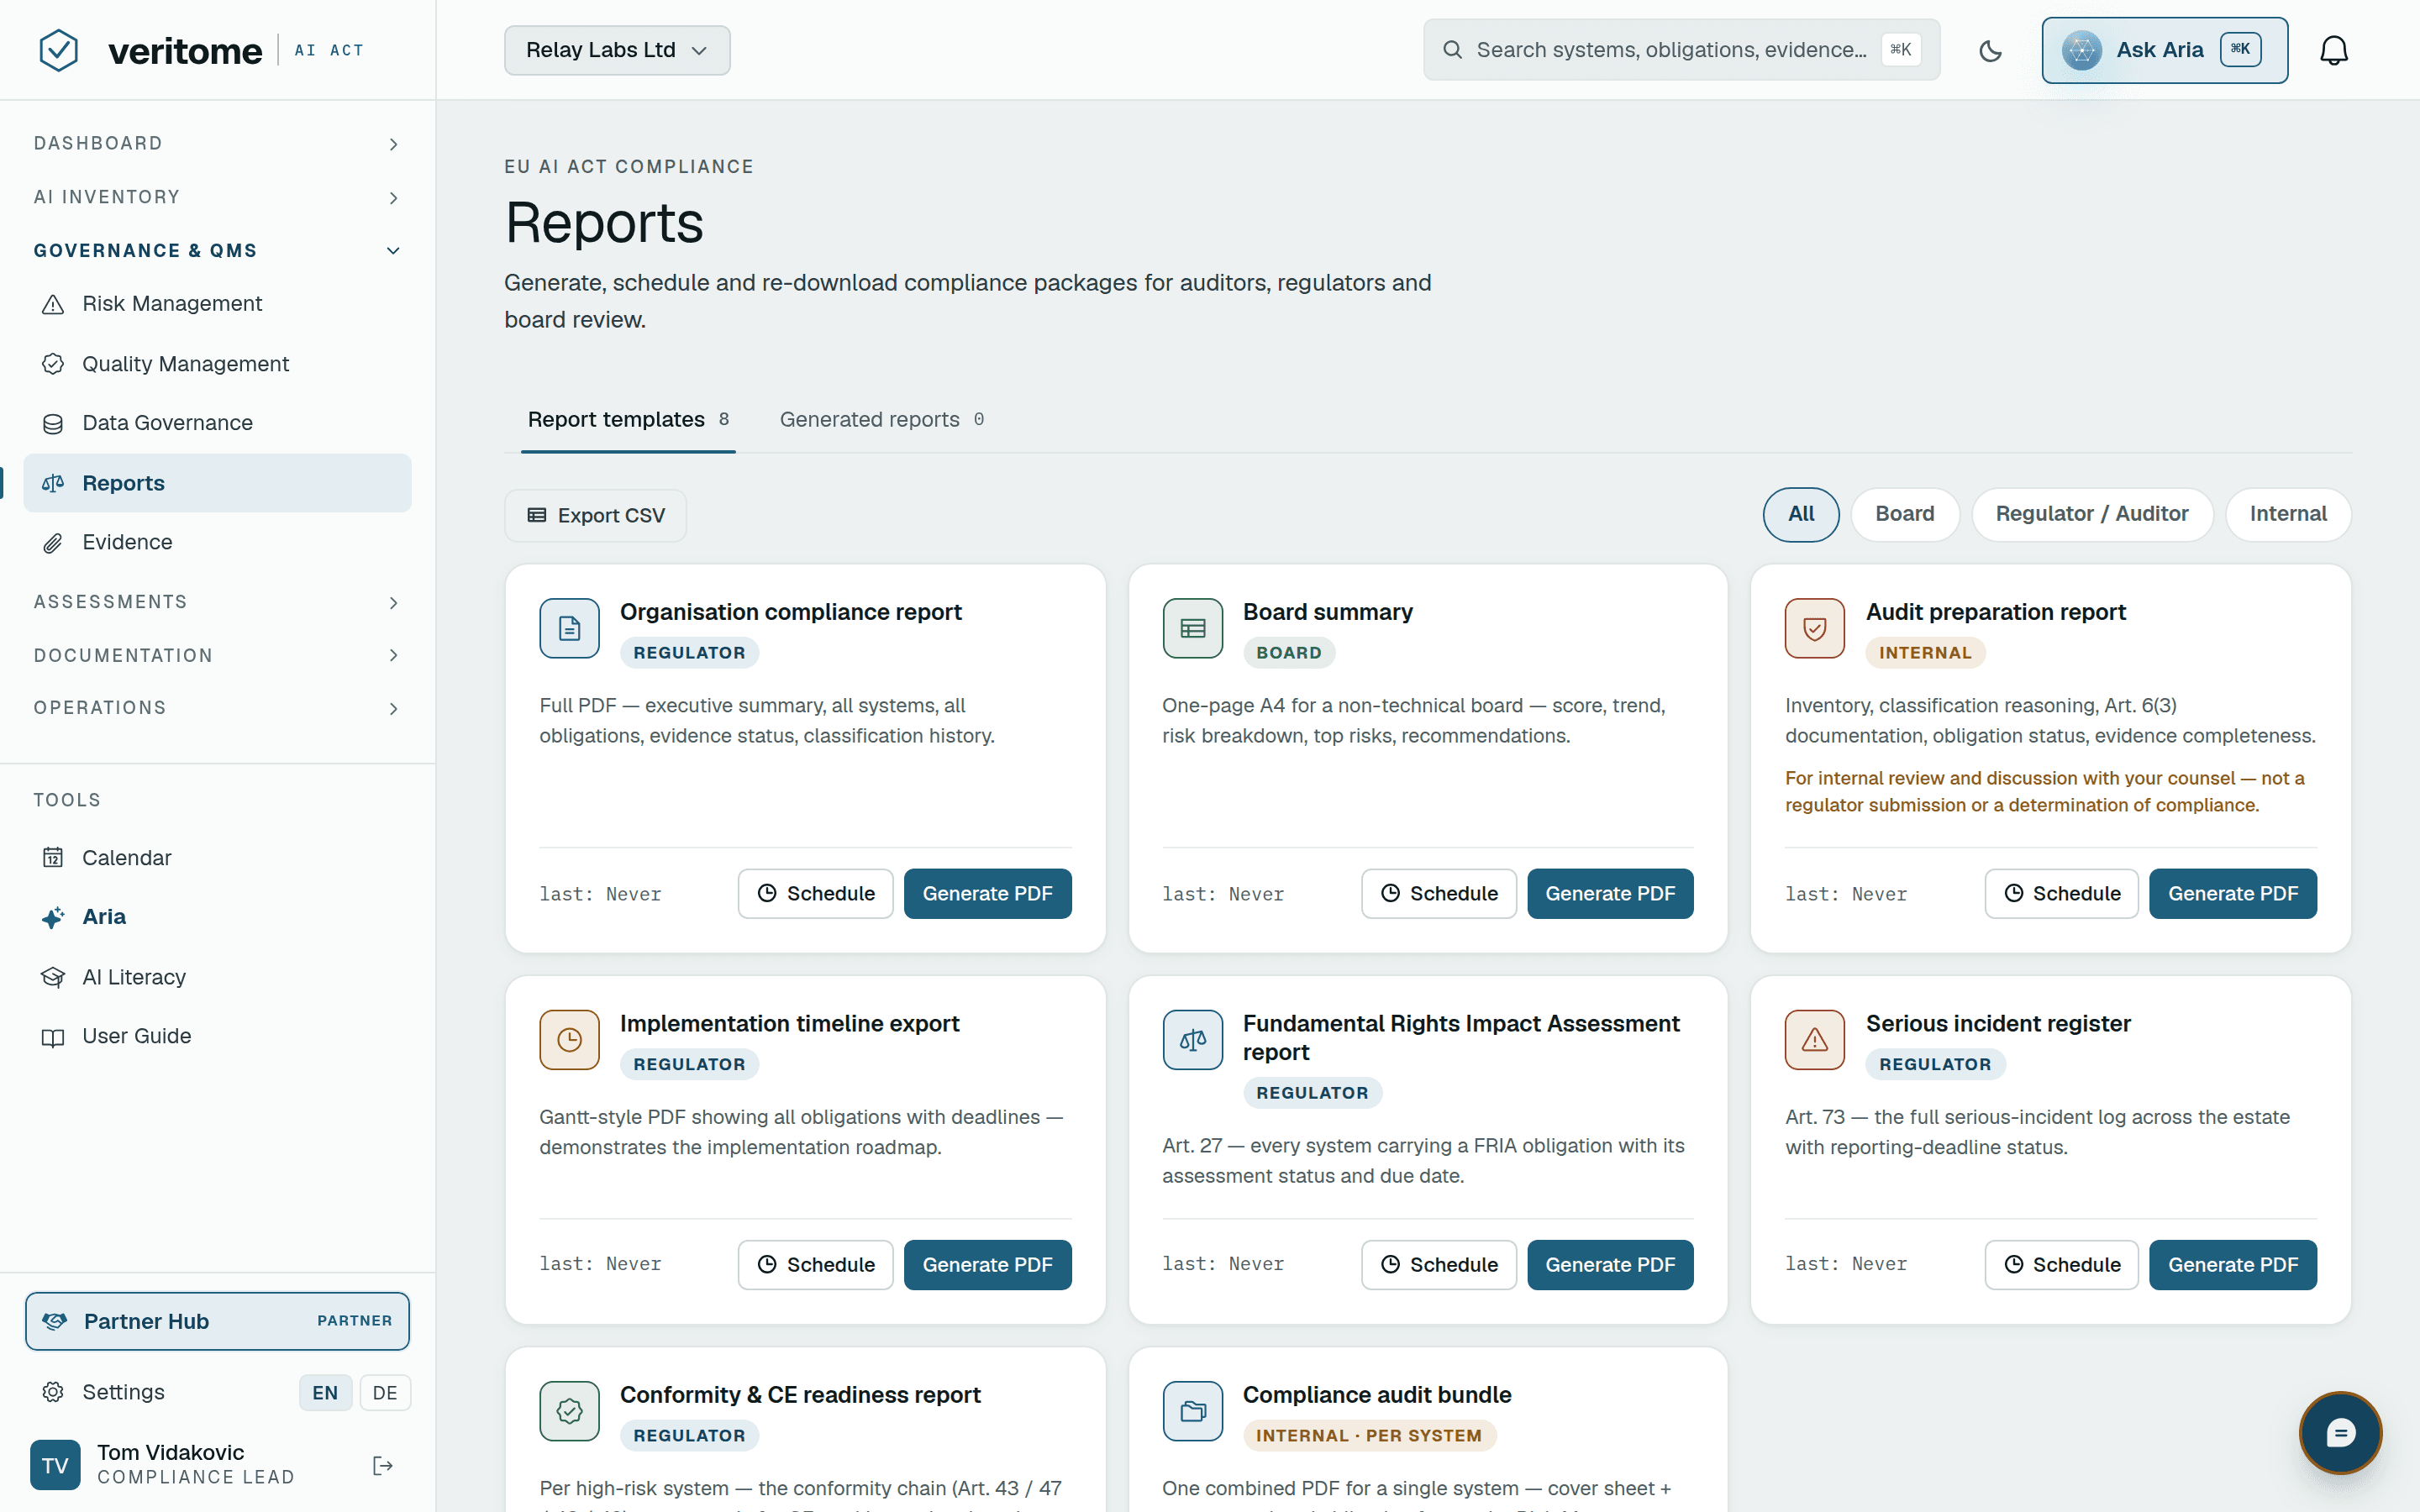
- GPAI obligations on internally fine-tuned models tracked separately from third-party deployments.
- The AI-literacy programme distributed across the group; completion per subsidiary.
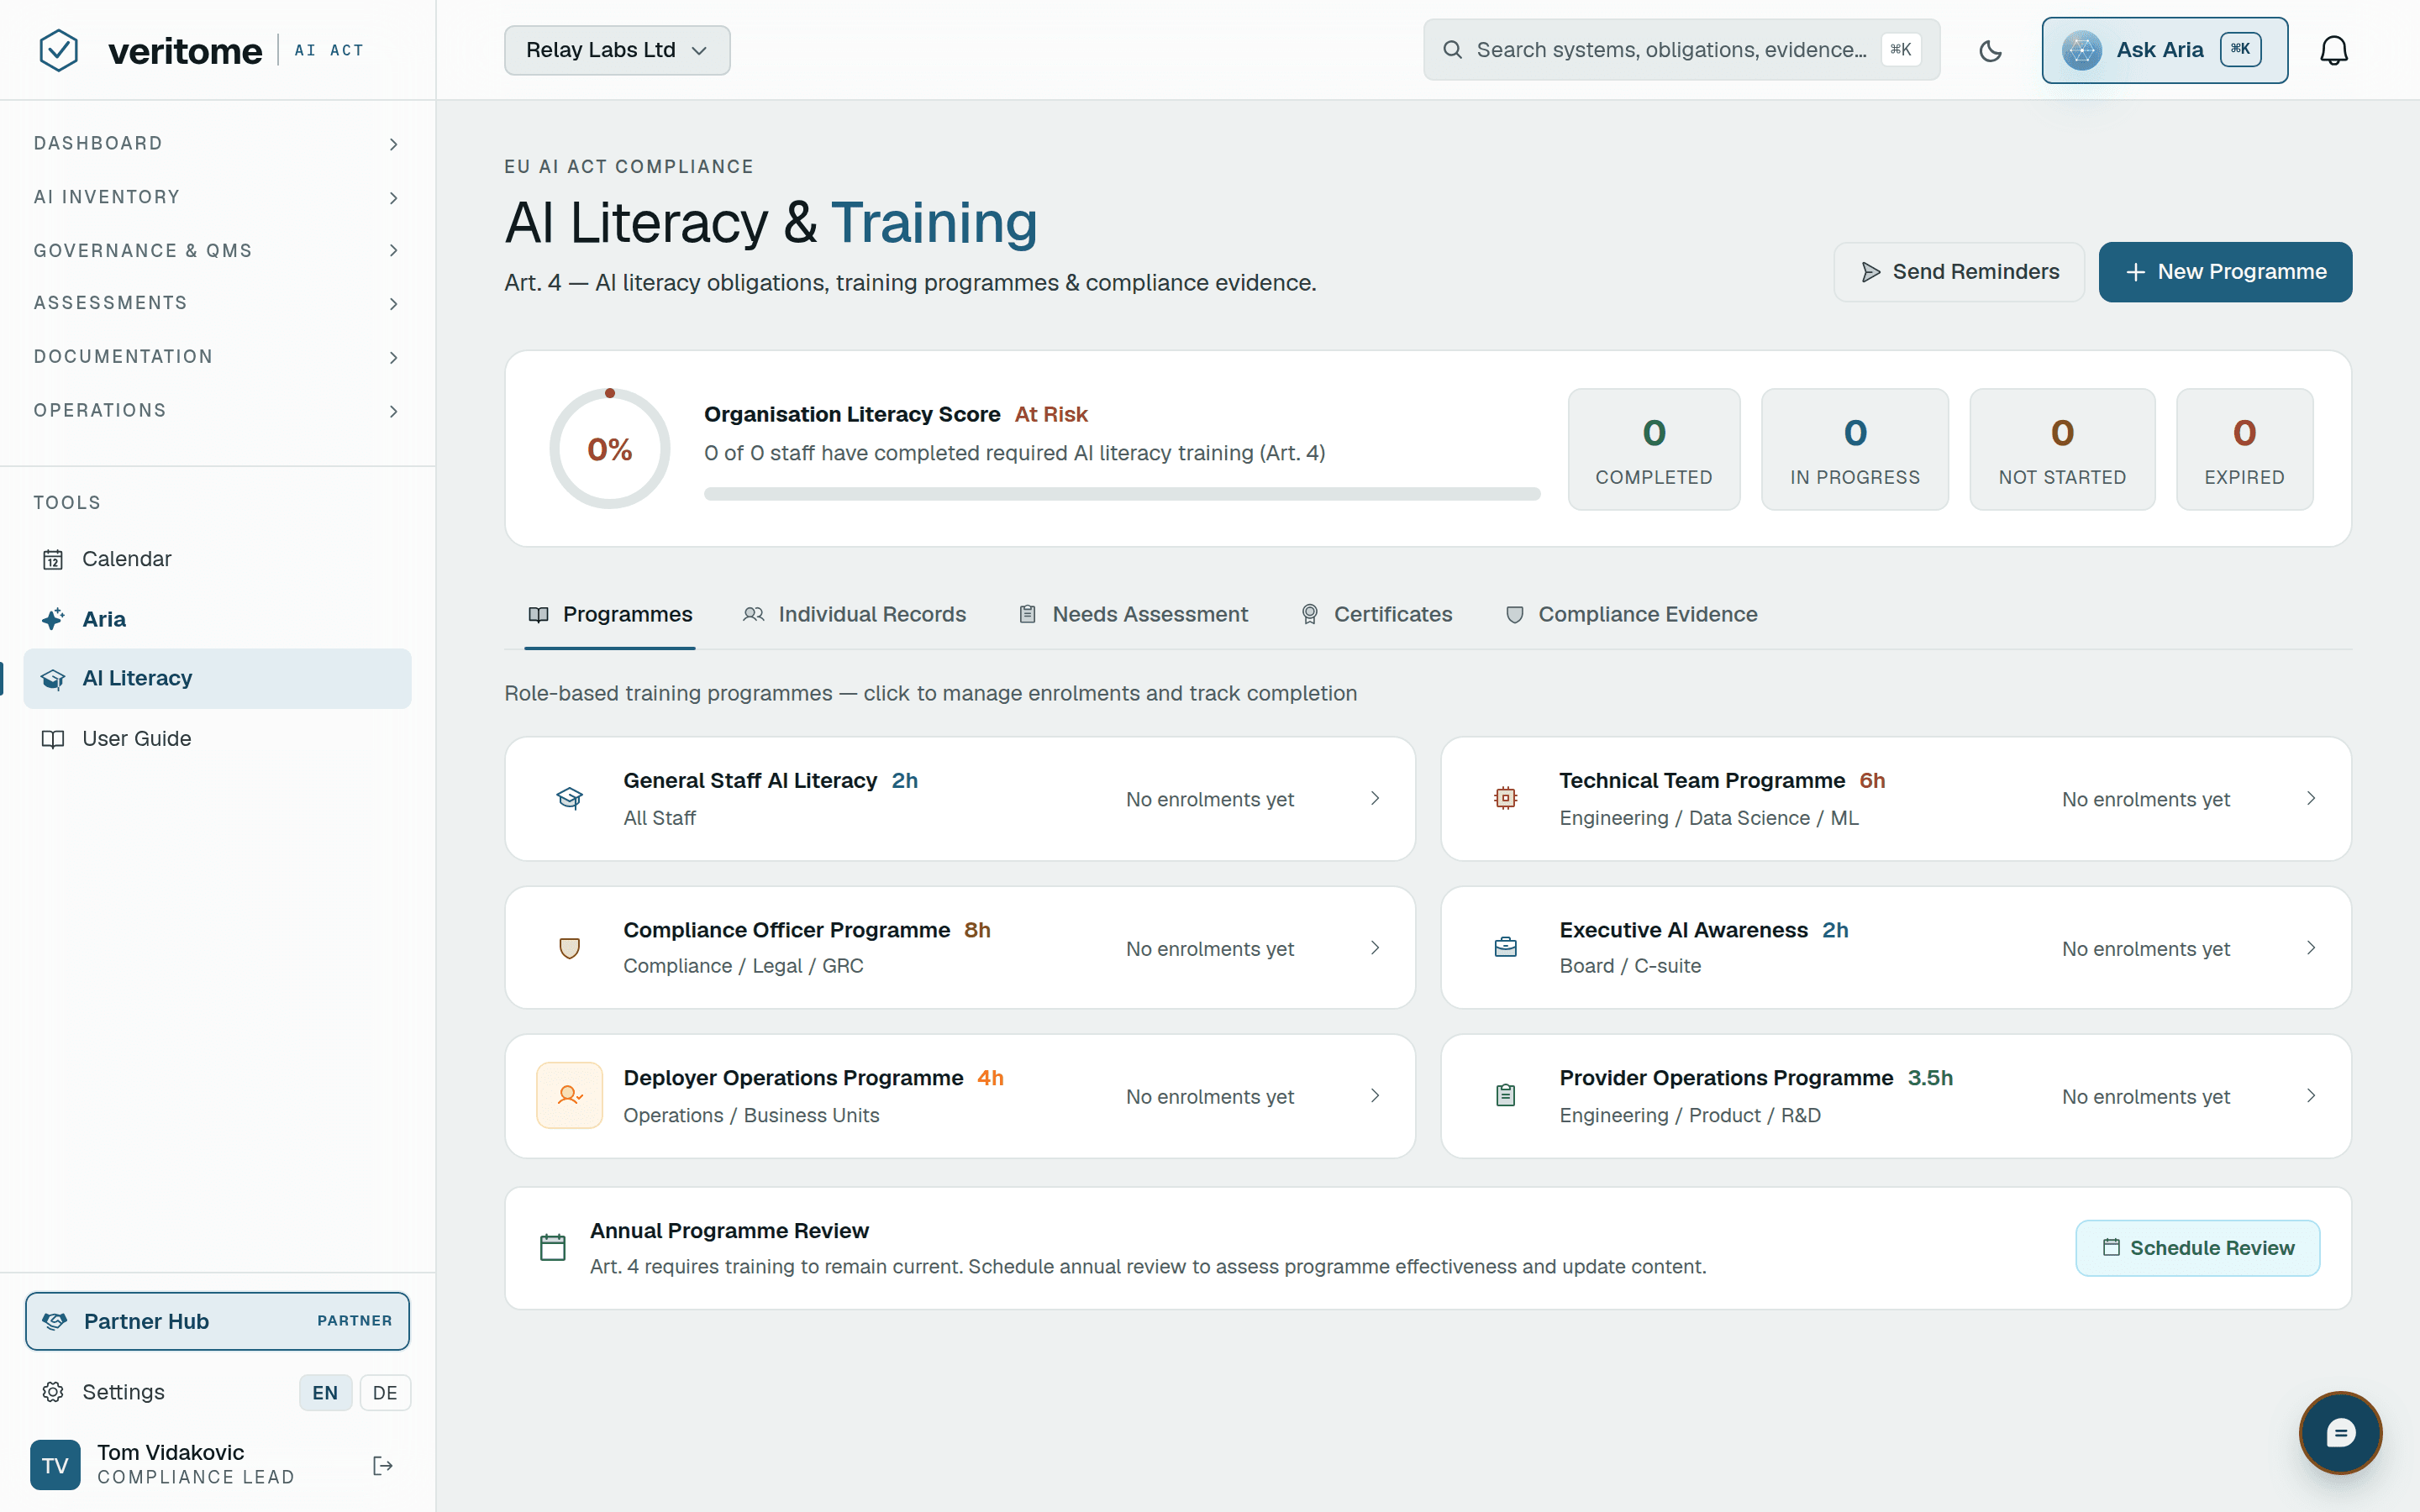
The capabilities that scale with the estate.
Questions groups ask
Can one instrument hold a group with several subsidiaries?
Yes. One identity, many organisations: each subsidiary keeps its own systems, classifications and obligations, and group compliance leads switch between them from one login. A group-level view rolls the estate up for the audit committee.
How does Veritome fit beside ISO/IEC 27001 and NIST AI RMF?
Both run as programmes on the same register. The clauses ISO/IEC 42001 and 27001 share are one record each, and a NIST AI RMF profile is generated for the counterparty who asks for one. Coverage is one matrix, exportable per framework.
Is there an API?
Yes — a REST API with an OpenAPI 3.1 specification, outbound webhooks for system, incident, obligation and evidence events, and an MCP server. Run Veritome beside ServiceNow, Jira or your GRC tool and share evidence both ways.
What does the board see?
The dashboard already has the numbers — portfolio completion, averages by risk tier, gate blockers, systems near completion — and the board summary is generated on a schedule as a sealed PDF. A prohibited system zeroes the portfolio; there is no hiding behind an average.